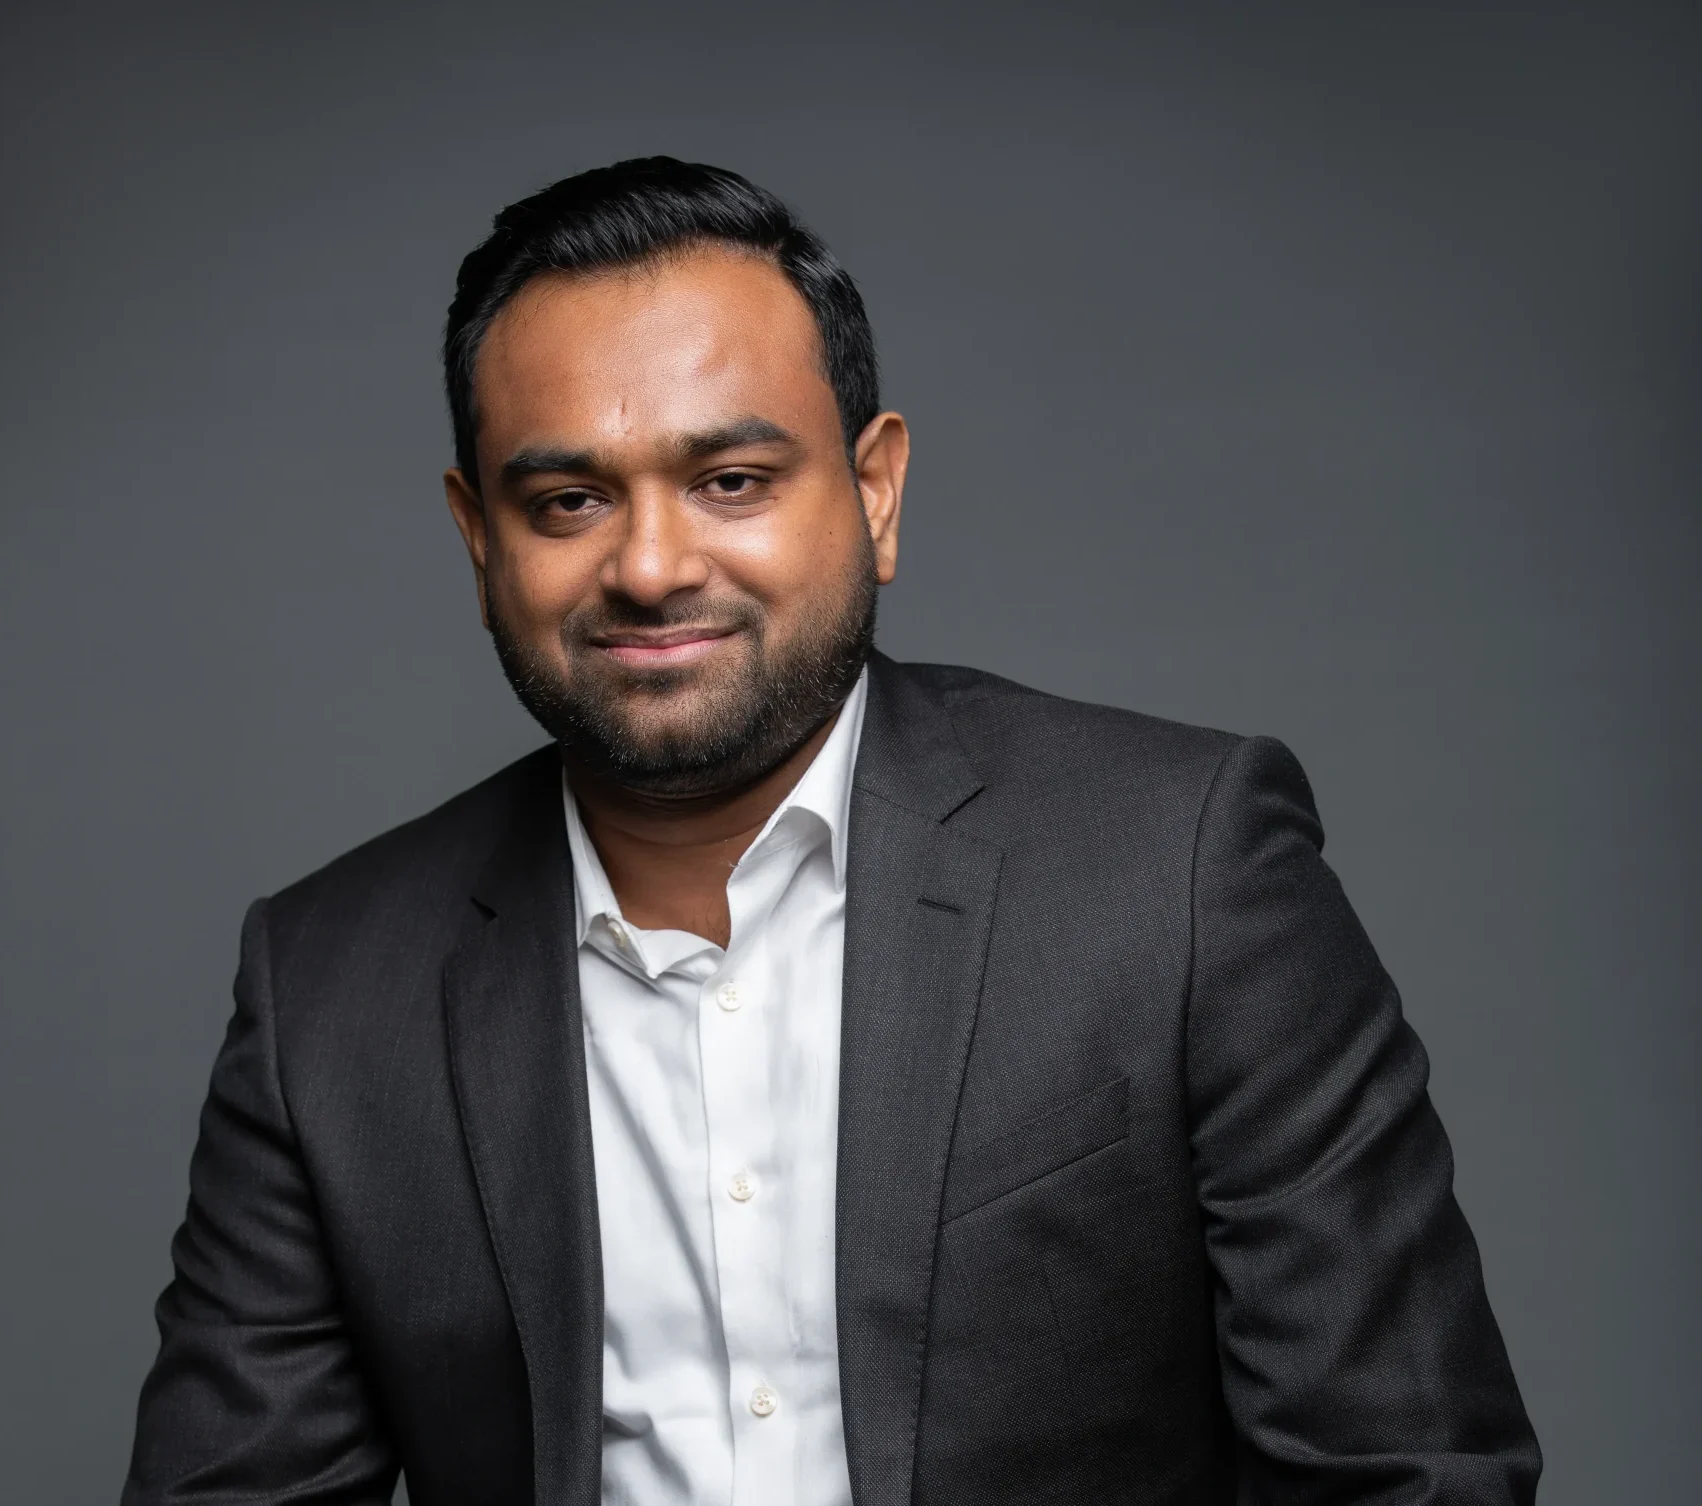
Techie.lk recently had the privilege of speaking with Asela Waidyalankara, a cybersecurity and technology professional with extensive experience in digital security, cyber resilience, data protection, technology policy and AI and digital governance.
His work focuses on helping organizations understand cybersecurity beyond the traditional IT function, with particular emphasis on risk, governance, resilience and responsible digital transformation.
He has been closely involved in discussions around Sri Lanka’s evolving cybersecurity landscape, including the Personal Data Protection Act, critical national infrastructure, AI-related risks and the development of cybersecurity skills.
Through his work and industry engagement, he advocates for stronger collaboration between government, industry and academia to build a more secure and digitally resilient Sri Lanka.
Waidyalankara on Sri Lanka’s AI Journey and Priorities
Where do you think Sri Lanka currently stands in its AI journey, and what should be the country’s top priorities over the next five years?
Sri Lanka is at an interesting point in its Artificial Intelligence (AI) journey. We have moved beyond simply talking about and are now seeing genuine experimentation. Universities are exploring AI, the private sector is investing in AI tools to improve workplace productivity, and people are increasingly experimenting with their potential benefits.
There is an important distinction between having access to AI tools and becoming an AI-ready economy. Because Sri Lanka has relatively good connectivity, access to AI tools is already possible for many, but becoming an AI-ready economy requires much more.
Sri Lanka has already done important groundwork through its broader digital-economy agenda, while work is continuing on the National AI & Data Strategy. The existing workstreams already recognize areas such as infrastructure, capacity building, Sinhala and Tamil datasets, startup enablement and AI-enabled government applications. The priority now should be disciplined execution.
There are five key priorities.
First is data. AI is only as good as the quality of the data available. Sri Lanka has significant amounts of data, but some of it is not digitized, while some digitized data is not machine-readable. Improving the quality, accessibility and usability of data is fundamental to developing effective AI systems.
Second is infrastructure. Connectivity remains important, but so is affordable access to computers and other devices. People need the necessary infrastructure to participate meaningfully in an AI-driven economy.
Third is people. Becoming AI-ready is not simply about producing more AI engineers or software developers. We also need lawyers, policymakers, educators and public officials who understand AI and its implications. Building broad AI literacy across society will be essential.
Fourth is governance. Sri Lanka needs responsible AI principles and clear systems for dealing with potential problems. Questions about accountability, safety and what happens when AI systems fail must be built into our national AI strategy.
Fifth is identifying problems where AI can genuinely improve people’s lives. Healthcare, agriculture, education and government services are areas where AI could deliver meaningful benefits. We should use AI because it solves real problems and improves peoples’ lives, not because it is fashionable.
Over the next five years, these fundamentals should shape Sri Lanka’s AI journey. If we can make progress particularly on data and people, we have a strong foundation. Sri Lanka has talented people capable of tackling complex problems, and bringing them into this process could help us find practical solutions that make AI genuinely useful.
Cyber threats have become increasingly sophisticated, affecting governments, businesses, and individuals alike. What do you see as the biggest cybersecurity risks facing Sri Lanka today, and are organizations prepared to deal with them?
One misconception is that the biggest cybersecurity risk is always a highly sophisticated attack. For most organizations in Sri Lanka, whether SMEs or listed companies, the key risks remain much more familiar: Compromised identities, phishing, social engineering, ransomware, poorly secured systems and systems that continue to operate beyond their intended lifespan. These often create a much wider impact than highly sophisticated attacks.
What has changed with AI is the speed and sophistication of threats. AI can make phishing, impersonation and social engineering far more convincing. In the past, people were advised to identify phishing emails through spelling or grammatical errors. That is no longer reliable. AI-generated messages can be grammatically perfect, natural and tailored with local context, making them much harder to identify.
At the same time, organizations have become increasingly digitally interconnected. Complex systems communicate with other complex systems, creating dependencies across organizations, suppliers and service providers. As a result, compromising one supplier or service provider can potentially have a significant impact across an entire ecosystem.
So, are Sri Lankan organizations prepared? The answer is uneven. Banking, telecommunications and technology organizations generally have more mature cybersecurity capabilities. Across the broader economy, including SMEs and some listed companies, cybersecurity is still often viewed as an IT problem rather than an organizational risk. That fundamental misunderstanding contributes to many threats organizations face.
The government’s center for cybersecurity, Sri Lanka CERT, which is responsible for protecting the nation’s cyberspace from cyber threats, has been expanding its capabilities as well, mainly through the launch of its National Cybersecurity Operations Centre (NCSOC). The NCSOC aims to strengthen real-time monitoring and coordination across government resources.
More importantly, the shift needs to happen at the management and board level. Organizations should ask: If our critical systems become unavailable tomorrow, how will we continue operating? That is more important than simply asking whether they need a firewall or antivirus software.
Overall, cybersecurity is not about preventing every attack. It is about ensuring that an attack does not become a catastrophe. Business operations should be able to continue despite an incident.
Once organizations understand cybersecurity through the lens of risk, resilience and business continuity, rather than simply technology, the conversation will become more meaningful, and Sri Lankan organizations will be better prepared.
Sri Lanka has introduced its Personal Data Protection Act, but many organizations are still adapting to its requirements. What progress have you seen so far, and what are the most common challenges businesses face in becoming compliant?
Sri Lanka was the first country in South Asia to pass a Personal Data Protection Act (PDPA), giving organizations a clear legal framework for protecting personal data, but the implementation process has faced delays and uncertainty.
Organizations have had several years since the Act’s passage in 2022 to begin preparing for it, with implementation expected by 2025. Amendments were subsequently introduced, creating further uncertainty over when the Act would become fully operational. The recent commencement order has now provided greater clarity, with key compliance provisions of the PDPA expected to come into full force 1 January 2027. The official Gazette covers Sections 2 and 3, Part I and Part III.
This is important because one of the biggest obstacles was the lack of a clear implementation date. Although the legislation had been discussed within business and professional circles, many organizations responded cautiously because they were uncertain about when compliance requirements would actually take effect. As per my observations, readiness remains uneven, with some organizations delaying preparations amid uncertainty over commencement dates.
The second major challenge is capacity and expertise. Under the Act, certain organizations will need to appoint a Data Protection Officer (DPO). This is a relatively new role for Sri Lankan organizations, and there is a misconception that it is primarily a legal position.
In reality, a DPO needs a much broader range of skills. They should have an understanding of the law, organizational processes, risk management and technology, while also being able to translate regulatory requirements into practical operational measures. At present, there are only a limited number of professionals with this combination of expertise.
Some organizations have recognized this gap and now offer training and development programs, but businesses should not assume that simply appointing a DPO will make them compliant. Data protection compliance is an ongoing process requiring changes to systems, processes, policies and organizational practices.
There is an important distinction between appointing a DPO and taking organizational responsibility for data protection, as well. Privacy and PDPA compliance require a “whole-of-organization approach,” and the responsibility should not be solely delegated to the DPO.
This will be particularly challenging for organizations that have spent years collecting and managing large amounts of customer data. Adapting existing practices to new privacy requirements, controls and legal obligations will take time.
Ultimately, the two major challenges for businesses will be people and organizational adjustment. With next year’s implementation deadline providing greater certainty, organizations now have a clear window to build expertise, review data practices and begin the journey towards meaningful compliance.
What needs to happen for citizens to have greater confidence in Sri Lanka’s digital ecosystem?
Trust is earned through behavior. Citizens cannot be expected to trust a digital platform simply because a government notice declares it secure or an organization tells them they must use it.
Digital trust has several dimensions. From a citizen’s perspective, particularly when using government services, people need to know what information is being collected, why it is being collected, who has access to it and what rights they have. These platforms must also be reliable, available and secure.
When something goes wrong, institutions must communicate transparently. With technology, incidents will inevitably occur, but treating a security or system incident as a reputational problem that should be hidden can seriously damage public confidence. Being open about problems and demonstrating how they are being addressed is essential to building trust.
Institutions such as the Data Protection Authority and Sri Lanka CERT also have an important role in strengthening this trust layer across the digital ecosystem.
Digital trust is also about fairness and inclusion. Digital transformation cannot assume that everyone has the latest smartphone, a strong internet connection or a high level of digital literacy, and it cannot assume that people of different ages and abilities have the same accessibility needs.
Digital trust sits at the intersection of security, privacy, transparency, accountability and inclusion. It is not a single box that can simply be ticked.
Most importantly, citizens need to feel that technology is being developed for them and that it is genuinely solving their problems. When institutions are responsive, transparent and accountable, and make a genuine effort to ensure accessibility and inclusion, adoption becomes much easier.
Digital trust is not about how sophisticated or complicated the technology is. It is about how institutions behave. If citizens see that technology is reliable, fair, secure and designed around their needs, they can become the strongest advocates for digital transformation themselves.
Critical infrastructure such as energy, finance, healthcare, and telecommunications have become increasingly connected. How vulnerable are these sectors to cyberattacks, and what measures should be prioritized to strengthen national cyber resilience?
When discussing critical infrastructure, we should not ask whether an organization can be attacked. We should assume that it will be attacked. This is why cyber resilience is important, and it is a national security and economic security issue, because modern economies depend heavily on interconnected digital systems. A failure in one system could potentially affect others, and the consequences could extend beyond individual organizations and potentially become national security concerns.
So Sri Lanka needs a clear policy and governance framework for identifying and protecting Critical National Information Infrastructure (CNII). The proposed Cyber Security Bill is an important policy instrument because it would allow certain organizations, whether in the public or private sector, to be designated as critical national infrastructure.
Once organizations are classified as CNII, authorities can identify their critical assets and establish minimum cybersecurity requirements. These could include security baselines, network and access controls, regular cyber drills and effective incident response and recovery plans.
Having a plan is not enough. Organizations need to test their plans regularly. The true measure of an incident response plan is not how good it looks on paper, but how effectively an organization responds when a real incident occurs.
This is particularly important for CNII because these systems form the foundation of modern life. A major failure in one area could potentially create cascading effects across other essential services.
Therefore, the focus should move beyond simply identifying vulnerabilities towards strengthening policy, governance, technical controls, processes and people.
One of the immediate priorities should be moving forward with the Cyber Security Bill and turning it into an effective legal framework. Industry stakeholders have already suggested changes and called for broader consultation. Incorporating appropriate stakeholder input will help create a stronger framework.
Legislative reform, in the form of much needed policy and governance structures, and practical security improvements should proceed in parallel to protect CNII. The objective of cyber resilience is to maintain critical services where possible, limit disruption and restore operations within tested recovery timeframes.
How can Sri Lanka develop a stronger pipeline of cybersecurity talent, and what role should universities, industry, and government play in that effort?
The first step in addressing Sri Lanka’s cybersecurity skills gap is to stop defining it simply as a shortage of people with cybersecurity degrees. Cybersecurity is a multidisciplinary field that requires engineers, incident responders, governance and risk professionals, auditors, lawyers, privacy specialists, threat intelligence experts, red-team practitioners and communications professionals. Building the right talent pipeline therefore requires a combination of skills rather than focusing on a single role.
From a university perspective, students need strong technical and theoretical foundations, but they need greater exposure to practical environments as well. Labs, simulations, research opportunities and practical cybersecurity exercises can help bridge the gap between academic learning and real-world requirements.
Greater collaboration between universities, including international partnerships, could also enrich this learning. Students would gain exposure to different approaches and experiences while developing people-to-people and international connections. This kind of interdisciplinary and cross-border collaboration can produce more well-rounded cybersecurity professionals.
Moreover, the industry has an important role in bridging the gap between graduates and employees. Many organizations already support internships, apprenticeships, mentoring and entry-level opportunities, but there is a contradiction when companies complain about a shortage of professionals while requiring several years of experience for junior positions. Organizations need to create realistic pathways for graduates to enter the profession and develop that experience.
AI is also changing the cybersecurity talent landscape. While AI can automate and accelerate certain tasks, there will continue to be areas where human intervention, oversight and judgement are essential. Developing experienced professionals who can make those decisions will therefore remain important.
Government and policymakers can support the ecosystem through a national cybersecurity skills framework, scholarships and opportunities for both local and overseas training. Public-private partnerships are particularly important. In many countries, stronger cybersecurity ecosystems and talent pipelines have been developed through collaboration between government, academia and industry. Sri Lanka should invest more heavily in these partnerships and capability-building initiatives.
Talent retention is another challenge. Sri Lanka has capable cybersecurity professionals, but once they gain experience, some may seek opportunities overseas. We should not necessarily try to prevent people from leaving to pursue career growth. Instead, we need to ensure that the next generation has similar opportunities to develop and that experienced professionals can continue contributing to the local ecosystem.
Creating centers of excellence, supporting research and development, and providing opportunities to work on cutting-edge cybersecurity challenges could help make Sri Lanka more attractive to experienced professionals.
Addressing the skills gap requires a long-term, ecosystem-wide approach. Universities must provide stronger practical exposure, industry must create realistic entry pathways, government must support skills development, and public and private sectors must work together. At the same time, Sri Lanka must be realistic about talent retention and focus on continuously developing the next generation of cybersecurity professionals.
Looking ahead, what do you think are the biggest opportunities, the greatest risks, and the policies or investments you believe could have the most transformative impact for Sri Lanka’s digital future?
I see the biggest opportunity in making everyday interactions with government and businesses simpler, more reliable and more accessible. For Sri Lanka, the value of digital transformation should be measured in practical terms: less time spent obtaining a service, lower costs for businesses, and better access to opportunities regardless of where someone lives or which language they speak. AI can support this, provided we apply it to clearly defined problems and assess whether it actually improves outcomes.
The greatest risk, in my view, is digitizing faster than we build the capacity to govern, secure and maintain these systems. Moving an inefficient process online can preserve its weaknesses. Connecting services without clear accountability, appropriate data protection and tested recovery arrangements can also increase the consequences of failure. We must take care that people who lack connectivity, digital skills or accessible services are not left further behind.
If I had to prioritize investment, I would focus on the foundations: Capable people, reliable digital infrastructure, well-governed data and institutions that can deliver consistently. That includes practical training for public officials, support for SMEs, Sinhala and Tamil language capabilities, and systems that can exchange information securely and lawfully. Cybersecurity and privacy should be built into procurement and service design from the outset, with clear responsibility for maintaining them.
Policy also needs to translate into delivery. I would favor a manageable set of priority initiatives with named owners, realistic budgets and outcomes that citizens can see. We should test services with the people who will use them, learn from their feedback and scale what works. Ultimately, success should be judged by whether technology makes people’s lives better and earns their trust.